On this page
Why does camera access still work?
You change the password, but the camera app on an old phone still opens live video from the network video recorder (NVR). The app may be using a session token held by an authorized device, while a shared user may have separate permission for remote viewing. The question is not whether the password changed. It is which access path the app is still using, and whether that path was revoked.
Why does the app work after a password change?
A password is normally checked when someone signs in. After a successful login, many systems issue a session token. The app stores that token and presents it during later connections. As long as the system continues to accept the token, the app may not need to send the new password or ask the user to sign in again.
Changing the password does not always invalidate every active session. Some systems revoke existing sessions immediately. Others leave them active until the user signs out, the token expires, the device is removed or an administrator selects a separate option such as sign out all devices. This difference explains much of the confusion around camera session tokens.
There can also be more than one identity involved. The account owner may change the cloud-account password while a family member, employee or property manager signs in through a shared-user account. That shared user’s credentials and permissions can remain unchanged. Removing the owner’s old password does not necessarily remove another person’s account.
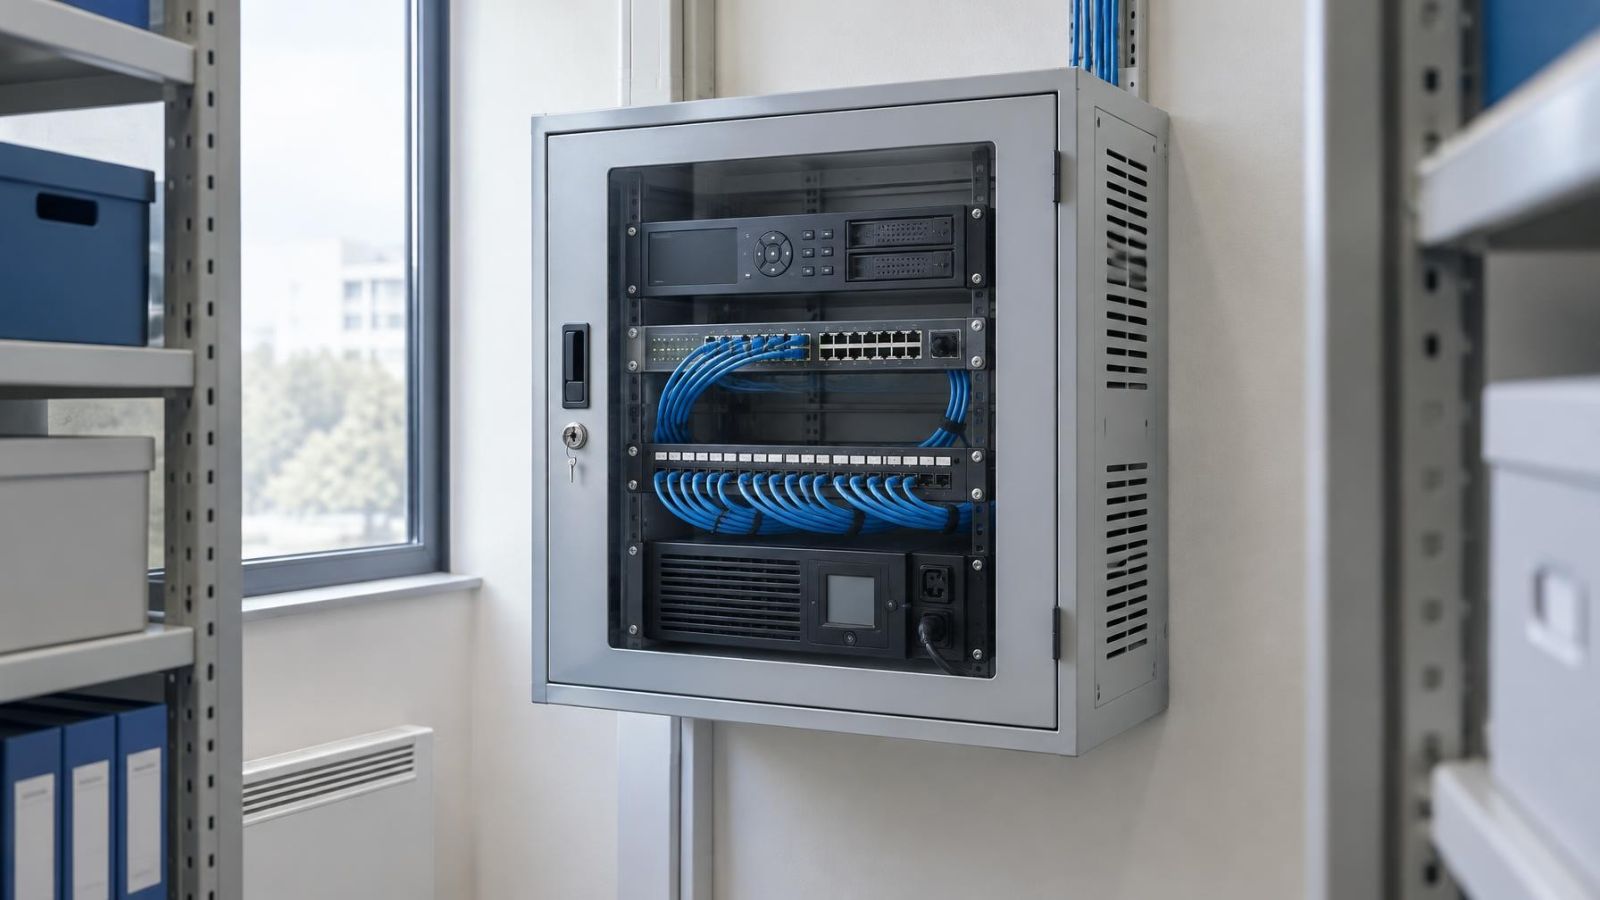
Local and remote connections also behave differently. On the same Wi-Fi or wired network, an app may connect directly to the NVR or security camera. Away from the property, it may use a cloud-assisted remote viewing service. A change to one set of credentials may affect only one route.
A successful password change proves that one credential changed. It does not prove that every session, user and device lost access.
Identify the remaining access path
Start by finding out whose identity the app is using and what it connects to. Avoid making several changes at once. If you change the owner password, recorder password and network settings together, you may stop the connection without learning which path remained open.
The common access paths are different controls, even when the app presents them on one screen:
| Access path | What authorizes it | What to inspect |
|---|---|---|
| Account owner login | Primary cloud-account credentials and active sessions | Session list, security settings and recovery details |
| Authorized device session | A token already stored on a phone or tablet | Device list, login history and session controls |
| Guest or shared user | A separate user identity or invitation | Shared users, roles and access permissions |
| Recorder or camera login | Credentials stored for the NVR, DVR or camera | Local device users and saved credentials |
| Local network connection | Direct access while connected to the property network | Wi-Fi state, local address and recorder connection mode |
The test conditions provide useful clues. If an old phone works on the property’s Wi-Fi but stops when Wi-Fi is disabled, it probably has local access rather than working remote access. If it continues over mobile data, a remote session, shared account or remotely reachable recorder connection is still available.
For an apartment, remember that the private home network and a building’s shared entrance system may be separate installations. Access arranged through a va’ad bayit or building manager should not be assumed to use the same account as cameras inside the apartment. A private home may similarly have separate credentials for a gate recorder, garden cameras and an indoor system.
Check every account and device
Open the account-management area from a device you control. Record what you see before removing anything. The labels vary, but look for sections covering users, shared access, authorized devices, active sessions, connected services and recorder users.
- Check every administrator account, not only the login used most often. An additional administrator may be able to create users or authorize devices.
- Review guest and shared-user accounts individually. Confirm the person’s name, role and the cameras or sites available to that account.
- Inspect the authorized device list for old phones, tablets, browsers and devices whose names are too vague to identify.
- Check household access separately from access given to cleaners, carers, tenants, employees or temporary staff.
- Review installer and property-manager access. Ongoing access should be deliberate rather than left in place because setup is complete.
- Confirm that the account owner controls the recovery email or other recovery method shown by the system. A password change can be reversed through a recovery route if another person controls it.
Device names are not always reliable. A phone may appear under a generic description, and reinstalling an app can create a new entry for the same physical device. Compare the list with the devices actually in use. Where the interface provides recent activity, use it to distinguish an active device from an abandoned entry without treating the displayed name as conclusive.
For a small business, check both personal phones and shared tablets kept at the premises. A device behind the counter may have access through the owner’s account even if staff members believe they are using a limited role. For a remotely managed property, include the local tablet, the owner’s current phone and any previous phone that was passed to another person.
How do you revoke camera access?
How do you revoke camera app access?
Use the system’s revocation controls as well as changing passwords. The exact menu names differ, but the objective is consistent: end active sessions, remove devices that should no longer be trusted, withdraw separate user permissions and update any independent recorder credentials.
- Make sure the account owner can sign in and controls the recovery details. Keep one known device available for administration.
- Use sign out all devices or revoke all active sessions if the option exists. Expect the current administrative device to be signed out as well.
- Remove unwanted phones, tablets and browser sessions from the authorized device list. If a device cannot be identified confidently, remove it and authorize the required device again.
- Delete or disable shared users who no longer need access. If the person should retain limited access, change the role or camera permissions instead of sharing the owner login.
- Change the NVR, DVR or camera credentials where they are separate from the cloud account. Update only the approved viewing devices with the new credentials.
- Sign back in on the devices that should remain authorized, then check that each one has only the intended sites, cameras and recordings.
Removing a device and removing a user are not interchangeable. Removing an old phone ends the authorization associated with that device, but the user may be able to sign in again if the account still exists. Removing a shared user ends that identity’s permission, but a locally stored recorder login could still provide another route.
The same distinction applies to the recorder. A camera app may contain both a cloud login and saved NVR credentials. Changing the cloud password may leave the recorder login untouched. Conversely, changing the recorder password can interrupt local viewing while an active cloud session remains listed as authorized.
How do you sign out camera sessions?
Use the account’s session or device-management screen rather than relying on an app’s ordinary sign-out button. Signing out on one phone usually affects only that phone. An account-wide sign-out or session revocation tells the service to stop accepting existing tokens. Follow it by removing unwanted authorized devices and reviewing shared users, because those controls may be stored separately.
Test that revocation worked
Revocation is confirmed only when the old device can no longer open the camera view or recordings. A confirmation message on the owner’s phone is useful, but it is not the test. Use the device that should have lost access and reproduce the connection conditions that previously worked.
- On the old device, close the app fully and open it again. Do not enter the new password.
- Turn off Wi-Fi and test over mobile data. This checks remote viewing without relying on the property’s local network.
- Try the live view, recorded video and any other camera group or site previously available. These functions can use different permissions.
- Reconnect to the property’s Wi-Fi and repeat the test. A device that fails remotely but works locally still has a local access path.
- Confirm that the app now requires a fresh login or reports that the session is no longer valid. Do not complete the login on a device that is meant to remain excluded.
- Review account activity, device lists and alerts for a new authorization or login attempt. Confirm that the removed device has not reappeared as trusted.
Testing both network conditions matters in Israel because many owners view a property from elsewhere while someone local uses its Wi-Fi. An overseas owner may successfully block remote access yet leave a tablet inside the apartment connected directly to the recorder. A shop owner may see the opposite: local viewing works at the premises, but the app cannot connect over mobile data because the remote session was ended.
If the old device still works, note exactly what remains available. Can it open live video but not recordings? Does it work only on Wi-Fi? Is it signed in under a named shared user? Does the device list show a newly authorized session? Those observations point to the control that still needs attention.
Decide who should retain access
Camera access is easier to manage when each person has a named account. Sharing the owner’s login may appear simple, but it makes later removal disruptive: changing one password affects everyone, and the device list may not show clearly who is viewing.
Keep the owner or administrator role separate from everyday viewing. A family member who only needs the entrance camera, an employee who checks the shop floor and a property manager who needs temporary viewing do not necessarily need the same permissions. Separate roles make access identifiable and removable without rebuilding the entire setup.
- Give each regular user a separate identity where the system supports it.
- Reserve administrative control for the person responsible for users, devices and recovery details.
- Set a clear process for removing old phones before they are sold, passed on or placed in storage.
- Review access when employees, tenants, contractors or property managers change.
- Keep recovery details under the owner’s control and check them whenever responsibility for the property changes.
- Document which credentials belong to the cloud account, recorder, individual cameras and local network. Do not assume one password covers all of them.
The useful end state is straightforward. Every person with access is identifiable. Every authorized device has a current purpose. Shared users have only the cameras and functions they need. The owner can revoke one person or one device without taking the whole system offline. A password change then becomes one part of access management, not the only control.
Key takeaways
- Changing a password and revoking an active session are separate controls.
- Authorized devices and shared users must be reviewed separately from the account owner’s login.
- Camera, recorder and cloud-account logins may use different credentials.
- Revocation should be tested from the old device over mobile data, not only on the property’s Wi-Fi.
- Each person should have identifiable access that can be removed without disrupting everyone else.